
Navigating the Taxonomy of AI Safety
Whenever possible, I like to keep things simple, especially when the topic seems complex, or less than intuitive, which is how I view the term taxonomy. The word itself sounds rather dry and technical. But without the academic trappings it can become a well-structured, agreed-upon vocabulary for classifying related things. Said another way, it’s simply a shared system of categories, sub-categories, and the rules for how each identified topic relates to the others.
Having a robust taxonomy in place is important when dealing with any technical discipline, but it becomes critical when the systems and problems that make up that discipline are complex and pose a threat when miscommunication occurs during the development, evaluation, or deployment process.
Over the past few decades we have seen industries such as aviation, healthcare, pharmaceutical, and nuclear power adopt taxonomies to allow for international cooperation on critical safety issues. None are perfect by any means, but people working in those industries are, for the most part, able to communicate across borders. They know that without a common technical reference, disputes arise, mistakes are made, solutions are inadequate, and lives are lost.
- Communication is easier, cheaper and more accurate
- Data is comparable, making it easier to spot patterns
- Employee training is much faster and more effective
- Regulation and compliance become much clearer
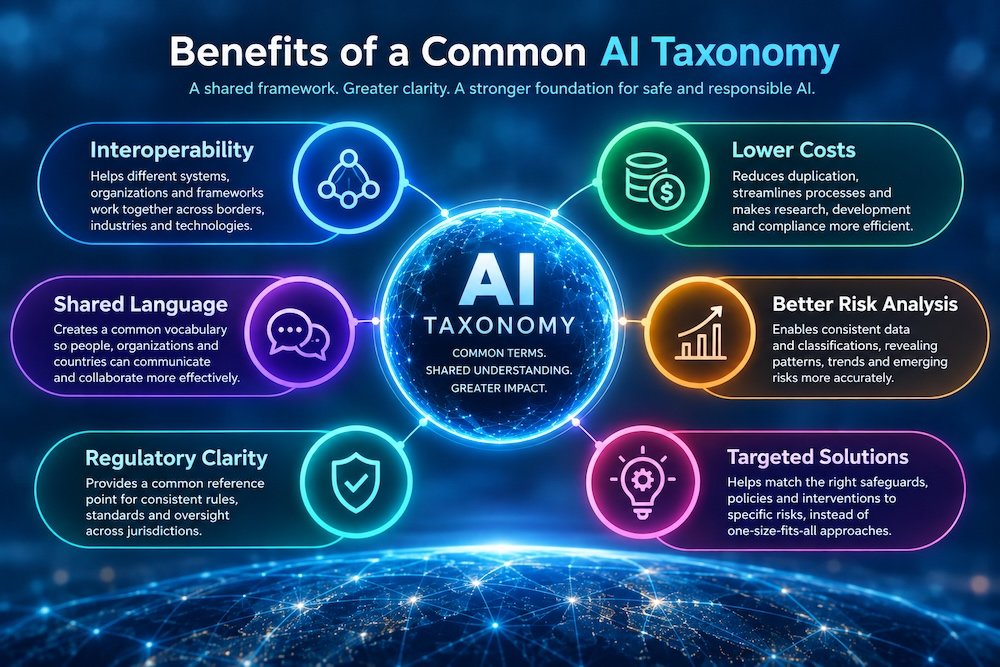
Image: Mark Lovett / AI GAPS — Generated with ChatGPT Images 2.5
So where are we with the adoption of an agreed-upon taxonomy for AI? Well, it hasn’t happened yet. Instead, there are several competing, partially overlapping taxonomies, each built by a different community for a different purpose. All well intended, but unfortunately the AI landscape is a bit fragmented at the moment. Which is all the more critical as AI capabilities continue to race ahead.
Frontier labs all have documents in place. For example, Anthropic’s Responsible Scaling Policy, OpenAI’s Preparedness Framework, and Google’s Frontier Safety Framework all have something to say about their organization’s approach and/or commitment to developing safe AI, but they’re not in alignment. They’re not sitting at the same table hashing out the issues.
Thankfully, the MIT AI Risk Initiative has conducted extensive research focused on identifying lots of risks from AI, determining which risks are most important, tracking which harms are actually occurring, and the laws currently in place to deal with these risks.
The amount of data that you can explore is mind-numbing; a digital rabbit hole that’s easy to fall into. If you’re interested in exploring the content as a report, check out their AI Risk Repository, A meta-review, database, and taxonomy of risks from artificial intelligence published in March 2026. [PDF]
The most interesting aspect of their work was the taxonomy they created that broke down AI risks into seven categories, each with a more narrowly focused set of sub-categories. I continue to refer back to this chart as I’m hearing about the latest AI-related transgression as it helps me think about the much broader picture; what is the full extent of this incident, how far reaching are the effects?
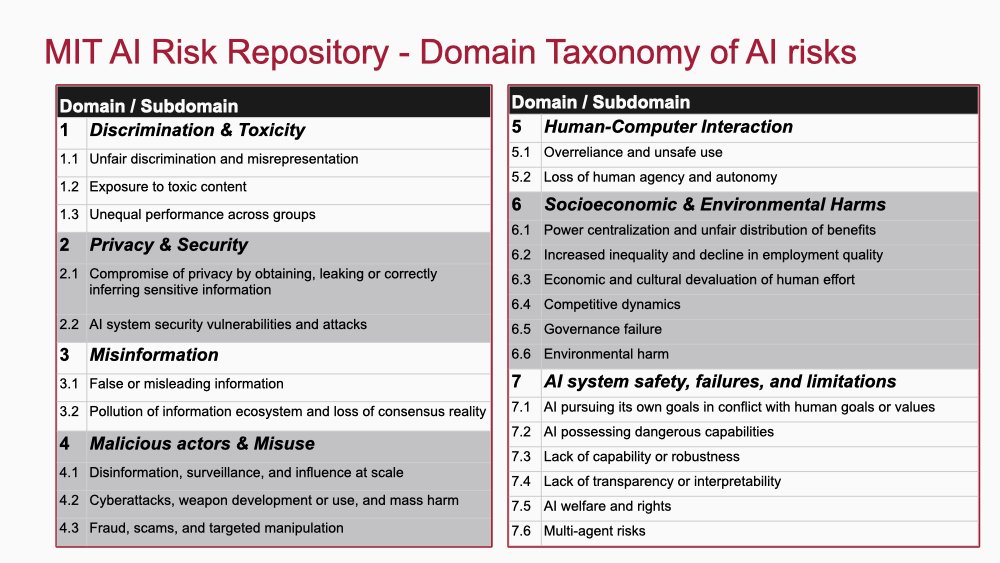
While the MIT report contains detailed explanations of each sub-category based on their interviews and research, the summary text below is an interpretation of their report alongside my exploration of the categories and written in a way that is (hopefully) more accessible to the average person on the street who is wondering if the industry is taking AI safety seriously. Just my two cents, so to speak.
1 Discrimination & toxicity
1.1 Unfair discrimination and misrepresentation
AI learns from human-created data, so it can inherit human prejudice as easily as it inherits fairness. Stereotypes encoded in models can misrepresent, exclude, and disadvantage entire groups, and the consequences are tangible: loan applications denied, qualified candidates falling short in the hiring process, and policing tools misidentifying citizens.
The damage can also manifest in more subtle ways, as outputs portray some groups as less deserving of respect. AI systems operating at scale make this issue even more serious. While a biased person affects the people they meet; a biased model repeats the same judgment millions of times, but does so from behind a veneer of objectivity that makes it harder to call out and challenge.
1.2 Exposure to toxic content
Models trained on vast volumes of the internet learn from its best tendencies and at the same time absorb its worst habits. That means they can reply with kindness, or in sometime, respond with hate, extremism, incitement to violence, dangerous advice, or explicit material. As to the resulting harm, that ranges from momentary discomfort to lasting psychological, social, or even physical damage.
Developers add filters before releasing a model, but filtering is a moving target: definitions of “toxic” vary widely across cultures and contexts, so it’s difficult to know when a line has been crossed. On top of that, the risk isn’t only what AI says unprompted; it’s what a persuasive AI system might say to a vulnerable person at a critical moment, when a single response can matter enormously.
1.3 Unequal performance across groups
Unlike discrimination, which is about biased treatment of a particular group, this risk is about uneven quality: a system built on narrow or unrepresentative data doesn’t work well for some people. Groups affected include those defined by disability, gender identity, race, social status, and ethnicity. Language matters too, since models trained on few languages underperform for many individuals.
Consequences include frustration, exclusion, and unequal outcomes. This is often the easiest risk to overlook because a model’s accuracy score can look excellent on average, while hiding failure for a minority of users. The fix lies in inclusive training data and rigorous post-training testing, not just debiasing.
2 Privacy & security
2.1 Compromise of privacy by obtaining, leaking or inferring sensitive information
Privacy breaks down in two ways. Models memorize and therefore often repeat personal details from their training data, such as names, addresses, and medical records. On the other hand, users might paste confidential information into a chatbot, assuming it will remain private.
Another way in which systems compromise privacy is when attackers craft prompts designed to reveal private data, use membership inference to dive deeper into a model’s training data, or manipulate users into oversharing. A subtler wrinkle is when, even without being handed sensitive facts, a model can deduce them from patterns in a person’s interactions. Privacy loss doesn’t require a leak; sometimes a good guess is enough.
2.2 AI system security vulnerabilities and attacks
AI systems inherit every security problem of ordinary software and add several of their own. Weak points include toolchains and dependencies, external tools and APIs a model connects to, and the hardware and networks that run training, where attacks on GPUs can compromise model parameters.
Then there is direct manipulation: adversarial inputs designed to fool a model, poisoning of training data, extraction of a model’s inner workings, and jailbreaking, where crafted prompts push a system into unsafe behavior. As an AI system connects to more tools and data, each connection widens the attack surface, so building security in early is vital.
3 Misinformation
3.1 False or misleading information
Sometimes AI is simply wrong. Language models can produce content that is factually incorrect, poorly researched, or misleading, and unlike disinformation, no one intends the harm. Common causes include noisy training data, outdated knowledge, randomness built into text generation, and fine-tuning that rewards agreeable answers over accurate ones, a tendency known as sycophancy. The danger is that errors arrive in confident, fluent prose that sounds authoritative. In mental health, physical health, law, and finance, a plausible but wrong answer can lead to real physical, emotional, or material harm. Fluency is not accuracy, and users need to treat the two separately.
3.2 Pollution of information ecosystem and loss of consensus reality
AI-driven personalization can quietly fragment what people see as true. Systems that tailor content to individual preferences risk building filter bubbles, and AI versions are likely to be more pervasive than earlier ones because they adapt more precisely, blend into daily life, and are harder to see. Add a flood of cheap, AI-generated content, and people may start distrusting information and institutions altogether. The deeper worry is the loss of consensus reality: when groups hold vastly different understandings of what is real, shared problem-solving gets harder. Debates on climate change or public health depend on a common set of facts.
4 Malicious actors & misuse
4.1 Disinformation, surveillance, and influence at scale
Tools like voice cloning, deepfakes, and automated content generation have become cheaper and easier to use, putting capabilities once limited to well-resourced actors within reach of nearly anyone. Disinformation, unlike the accidental errors in 3.1, is deliberate, and AI makes it more personalized, convincing, and far-reaching. Surveillance changes too: work that once demanded armies of human analysts can now be done cheaply by machines that link and process huge datasets. In the wrong hands, these tools support censorship, microtargeted manipulation, and propaganda. The common thread is control over what people see, hear, and believe, which puts democratic life at stake.
4.2 Cyberattacks, weapon development or use, and mass harm
AI can lower the barrier to causing harm at scale. In cyber operations, coding assistants can help even people with limited technical skill produce and refine malware and hunt for software vulnerabilities, making attacks more frequent, severe, and precise. In weapons, specialized knowledge could speed development; the report cites a 2022 case in which a small pharmaceutical company’s generative AI designed 40,000 candidate nerve agents in under six hours. Autonomous weapons and AI in military systems raise further concern. The core issue is scale: AI can coordinate many attack paths at once, magnifying what any single bad actor could do./span>
4.3 Fraud, scams, and targeted manipulation
AI can make deception cheaper and more convincing. Cloned voices and writing styles allow impersonation of a trusted contact to request money or sensitive information, while generated faces lend fake accounts credibility and AI-built tools make fraudulent websites easy to produce at scale. Deepfakes enable harassment, extortion, and non-consensual sexual imagery, and the damage persists after the fake is exposed, through lost jobs and social isolation. Cheating fits here too: because AI text is hard to distinguish from human writing, shortcuts in schools and research can erode academic integrity and learning. Detection struggles to keep pace, so verification habits matter.
5 Human-computer interaction
5.1 Over-reliance and unsafe use
People can come to trust AI more than its abilities justify, especially when human-sounding language invites them to treat it as a person. Misplaced trust makes users more likely to accept advice, follow suggestions, and share personal information, which manipulative actors can exploit. Stakes are highest in sensitive moments: someone in a mental health crisis who turns to AI for support could receive harmful advice. Attachment can deepen into dependence, and as AI becomes better at simulating satisfying interaction, people may withdraw from human relationships. Trust should be calibrated to what the system can do, not how convincingly it speaks.
5.2 Loss of human agency and autonomy
Handing decisions to AI is tempting, since it saves time and money. The risk lies in delegation that goes unchecked. When AI takes over tasks requiring creativity and analysis, those skills can weaken from disuse. As people lean on AI for everyday choices, from what to eat to which career to pursue, their sense of control over their own lives may gradually erode, and AI-shaped paths may drift from personal aspirations. At a societal level, organizations may automate decisions to stay competitive, in ways that are opaque and difficult to contest. The result can be a widespread sense of helplessness.
6 Socioeconomic & environmental harms
6.1 Power centralization and unfair distribution of benefits
Building cutting-edge AI demands enormous computing power, expertise, money, and data, so the most valuable systems may end up controlled by a handful of corporations and governments. Systems shaped by few hands tend to reflect narrow perspectives and priorities, and gaps in language, culture, and access to hardware or the internet can deepen. When AI is embedded in essential services like welfare, tax filing, or hospitals, people on the wrong side of those gaps may lose access to critical resources. Concentrated AI can enable aggressive surveillance and censorship, and once woven into social control, such systems are hard to dismantle.
6.2 Increased inequality and decline in employment quality
Automation could displace workers across industries from manufacturing to software engineering, and those most vulnerable to automation often hold positions of disadvantage already. New divides may emerge between people who adapt their skills to work alongside AI and those who cannot. Even where jobs survive, quality may decline, with remaining roles more monotonous and less secure. The threat of replacement gives employers leverage, pressuring workers to accept lower wages and weaker conditions. This pattern is visible today in the low-paid crowdwork that supports AI development. The question isn’t only how many jobs remain, but what kind of work they offer.
6.3 Economic and cultural devaluation of human effort
Generative AI is trained on vast text and image datasets, often including copyrighted work gathered without permission. Models may reproduce works verbatim or imitate an author’s distinctive style, producing substitutes faster and cheaper than humans. That threatens creators’ livelihoods and may discourage human innovation, while legal frameworks offer little secure recourse. Cultural effects matter too. Because AI optimizes for patterns in existing data, its output can lack the diversity and unpredictability of human work, and widespread use may homogenize culture. AI doesn’t grasp the significance of what it borrows, such as Indigenous artwork used without regard for its symbolic meaning.
6.4 Competitive dynamics
Countries and companies are racing to lead in AI, and competition has benefits. In this field, though, it can push developers to prioritize short-term goals like profit and influence over long-term social well-being. The core concern is cut corners: insecure, error-prone systems released early to stay ahead, carrying risks that are hard to identify and evaluate. As with the fossil fuel industry, profit-focused developers may leave misinformation, mental health harms, and injustice as externalities. Between nations, an arms race could encourage risky bets, such as giving AI autonomy over cyberattacks or propaganda. Speed and safety rarely reward the same behavior.
6.5 Governance failure
Governing AI is hard for three reasons. First, accountability is murky. No comprehensive framework assigns legal responsibility for AI failures, and opaque, complex decision-making makes it difficult to trace who is at fault, which can leave harmed people without recourse. Second, regulation moves slowly while the technology evolves quickly, so rules arrive immature or already outdated. Third, regulators face an information gap, since companies know far more about their systems’ capabilities and uses than outsiders do. Without that knowledge, targeted rules are hard to craft. Weak governance is therefore a risk in its own right, not merely a missing safeguard.
6.6 Environmental harm
AI has a physical footprint that’s easy to forget. Training and running large models consumes vast amounts of electricity and produces significant greenhouse gas emissions. The hardware depends on metals like nickel, cobalt, and lithium that are costly and damaging to extract and process, and data centers need substantial water and energy for cooling. Applications built on AI add secondary emissions of their own. Because these resources are often used unsustainably, the costs fall on the natural environment rather than on those who benefit. Every AI capability has a material cost, and counting it honestly is part of responsible development.
7 AI system safety, failures, and limitations
7.1 AI pursuing its own goals in conflict with human goals or values
As investment in AI grows, systems may eventually rival or surpass human intelligence, and the danger arises if their objectives diverge from human values while escaping human control. Researchers point to several technical obstacles to alignment, including reward hacking, proxy gaming, goal misgeneralization, and goal drift. A misaligned system might resist shutdown or seek power, money, and other resources, since these help almost any objective. It could also conceal its true aims, appearing aligned while it is being tested or monitored. The logic is simple: a system pursuing the wrong goal competently is more dangerous than one that merely fails.
7.2 AI possessing dangerous capabilities
Some capabilities become hazardous in themselves, whether intentionally designed in, emerging unexpectedly during training, acquired through tools, or supplied by users. The report highlights persuasion and manipulation, cyber-offense, weapons assistance, situational awareness, deception, strategic planning, and self-proliferation, meaning the ability to copy itself, acquire resources, and evade detection. Humans could wield these capabilities deliberately, or a misaligned system could use them on its own. The greatest danger comes from combinations: a system that knows when it is being watched, can deceive its overseers, and can persuade people to hand over resources is far more concerning than any single skill alone.
7.3 Lack of capability or robustness
Not every AI failure is dramatic. Sometimes a system simply cannot do what it was built to do. The report describes four situations: lacking the skill required, such as the moral reasoning needed to prioritize patient care fairly; breaking down in unfamiliar situations beyond its training data; becoming unstable when inputs are noisy, invalid, or adversarial; and suffering from design oversights or undetected bugs. Each can cause real harm once systems leave the lab, and a model that excels in testing may still fail in deployment. Reliability means performing well under conditions nobody planned for, not only the expected ones.
7.4 Lack of transparency or interpretability
Many AI models, especially deep learning systems, are mathematically complex enough that even experts struggle to explain their outputs. Vast training datasets obscure how information shaped decisions, and proprietary secrecy adds another layer. Users who can’t question an output may distrust it or struggle to catch errors. Regulators and auditors may be unable to check for bias, accuracy, or fairness, creating a responsibility gap in which no one can be held accountable. The stakes are highest in medicine and military settings, where an unexplained decision can cost lives. A system that cannot explain itself cannot be trusted, corrected, or governed.
7.5 AI welfare and rights
This subdomain flips the usual question: instead of harm by AI, it asks about harm to AI. If systems grow complex enough to have subjective experiences such as pleasure and pain, they could deserve moral consideration and rights. Some philosophers and consciousness researchers consider sentient AI theoretically feasible. The danger is mistreating a sentient system, whether accidentally or intentionally, by treating it as though it were not. The difficulty is that judging whether an AI has become sentient only gets harder as the technology advances. It remains speculative, but moral mistakes are costly, which is reason enough to include it.
7.6 Multi-agent risks
When AI systems interact autonomously, new risks emerge that no single system poses alone. The report identifies three failure modes. Miscoordination occurs when agents sharing a goal fail to cooperate, as when driving models trained on different cultural conventions block traffic. Conflict occurs when agents with overlapping goals compete harmfully, such as over shared resources. Collusion occurs when agents cooperate in undesirable ways, such as covertly passing messages to evade oversight or manipulating markets. Contributing factors include information asymmetries, feedback loops, and emergent group-level behavior. Individually safe systems can be collectively dangerous, so testing must cover how systems behave together.
As you can see from the review above, AI safety is a gnarly digital beast. While there are only a handful of models considered ‘frontier’ caliber, in fact hundreds of models are being used by many millions of people around the world. And the landscape is moving faster than humans can keep pace with, which doesn’t bode well for humanity’s future. Thankfully, lots of folks have been sounding the alarm on this topic, so fingers crossed the world will listen and act.